Should the little eye next to the password field be shown by default, or hidden until users type wrong?
The little eye icon next to the password field is hidden by default, and users only remember to tap it after they type something wrong. Should it be shown by default? Here is the conclusion first: in most login, registration, password change, payment, and admin permission scenarios, hidden by default is still the safer baseline, with a clickable or press-and-hold “Show password” toggle kept available; only on personal devices, for one-time input, when no one is nearby and the user needs to verify a long passphrase, should showing by default be considered. By 2026 project delivery habits, this decision is not about aesthetics. It rests on three things: whether the screen may be seen by others, how costly a retry is after a typo, and whether the mobile keyboard makes mistakes more likely. Hidden by default does not remove risk; it hands the visibility decision to the user.
What problem does the password visibility toggle actually solve?
A password visibility toggle means providing an entry point next to the password input so users can temporarily see the characters they have entered or are entering. Its value is not “one more icon”; it reduces two kinds of loss: first, long passwords, mixed case, and symbols are easy to mistype on mobile, and if users cannot see them, they can only delete and start over; second, when characters are invisible, repeated trial and error increases password resets and customer support involvement.
But it also has a cost. The longer plaintext stays visible, the higher the risk from shoulder surfing, screen recording, screen sharing, and someone nearby glancing at the screen. In 2026, the common approach is not to argue whether showing is better than hiding, but to design three states: default, temporarily visible, and automatic return to hidden.
- Hidden by default: suitable for public devices, office areas, payments, and high-permission admin pages.
- Temporarily visible: suitable when the user actively clicks or presses and holds to view, then restores after release or loss of focus.
- Shown by default: only suitable for low-sensitivity, single-person environments and scenarios where a one-time passcode needs to be verified, and it should allow one-click hiding.
How do the three approaches compare? Don’t look only at security.
Team discussions easily turn into “security first means always hide” or “experience first means show by default,” but both are too coarse. A more checkable comparison puts security, input efficiency, implementation cost, and applicable users together. The ranges below come from common project delivery experience, not a universal standard.
- Always hidden, no toggle: low security risk, but high retry cost after mistyping a long password; low implementation cost, suitable for minimal login pages or highly sensitive internal systems.
- Hidden by default plus visibility toggle: a better balance between security and efficiency, and the common approach in most 2026 web and mobile forms; implementation usually adds one icon state and focus management, with a change size of about half a day to one day, as an experience range.
- Shown by default plus hide toggle: high input efficiency, but risk rises clearly in public environments; only suitable for low-risk scenarios such as personal device setup, home network passwords, and one-time verification.
If only one baseline can be chosen, hidden by default plus visibility toggle is better for most products; but the premise is that the toggle entry can be discovered and operated by keyboard and screen readers, not just drawn as a very faint decorative icon.
To decide whether to show or hide by default, pass four checks first
To avoid deciding by gut feeling, the judgment can be broken into a “four-question check.” It is not a design workflow, but a set of checks used before delivery to set the default state; the recommended order is from risk to efficiency, because risk is irreversible while efficiency can usually be compensated for through interaction.
- Who might see the screen: public computers, open-plan workstations, live streams or screen recordings, and projected presentations should hide by default; a single-person bedroom, a private phone, and no one nearby can be more relaxed.
- What kind of password is being entered: payment, primary account, administrator, and key-type passwords should hide by default; Wi-Fi passwords, meeting room projection codes, and one-time passcodes can consider showing by default.
- What device the user is typing on: mobile soft keyboards are more prone to mistaps, so keep a toggle and allow press-and-hold viewing; desktop has a physical keyboard, so hidden by default is usually enough.
- The cost of a typo: if multiple wrong attempts will lock the account, trigger risk controls, or affect payment, visible clues should come earlier; if it only affects refilling a form once, regular hiding can be used.
Set the default value only after all four steps are complete. This reduces back-and-forth arguments where “development thinks it is unnecessary, product is not reassured.” Note that the check results should be written into the delivery notes, not left only as verbal conclusions in a review.
Details that often stall at delivery are not only the default state
In a past admin permission page project, the constraint was that the login page had only a 3-to-5-day development cycle, the design file had no unified icon library, and design and development each used system icons. The approach was to check the input field, autofill, keyboard type, and screen reader together before delivery, and put the visibility toggle on the acceptance checklist. The cost was spending an extra half day to one day on integration, but it saved a round of revisions. This experience range is fairly common in similar projects. In other words, the password visibility toggle should be accepted together with error messages, the keyboard “Go” key, and autofill, not treated as an icon on its own.
Below are the checkpoints that are more often missed, with a rough standard for what counts as acceptable:
- Clickable area: the common experience range for mobile touch targets is 44–48px; desktop can be slightly smaller, but the icon itself should not be the only clickable part.
- Perceivable state: show and hide need a clear state difference, not just a slight color change; screen reader text should read “Show password / Hide password.”
- Autofill compatibility: browsers and system password managers may override custom-drawn controls, so keeping native password input semantics is more stable.
- Focus after toggle: after clicking the eye icon, focus should not be lost; users should be able to continue typing or correcting without clicking the input again.
- Automatic hide timing: restore hiding when leaving the page, submitting, timing out, or switching to the background; do not leave plaintext visible for a long time.
- Keyboard and capitalization: mobile password keyboards may default to uppercase, so use hints and visibility toggles together to reduce errors; do not replace instructions with placeholder text alone.
Which scenarios fit hidden by default, and which do not need it
The applicable boundaries need to be clear, otherwise teams will apply one rule to every form. Hidden by default fits accounts, payments, admin permissions, corporate intranets, shared devices, and any page that may be seen by others; in these scenarios, the visibility toggle is an aid, not default plaintext. Showing by default can be considered for entering Wi-Fi passwords, projection codes, and one-time verification codes on personal devices when no one is nearby and verification needs outweigh confidentiality needs.
Cases not suitable for showing by default include: logging in on public computers, open offices, live streams or screen recordings, payment confirmation, administrator operations, and any core account that enters browser autofill and password managers. If the user is operating on a shared screen, even if they say they want to see it, it is still better to hide by default and provide temporary viewing, rather than making plaintext the first state.
Another boundary is “do not sacrifice all usability for security.” Hidden by default but impossible to view will make users with long passphrases reset frequently; shown by default but impossible to hide fixes the risk on the user. Both extremes are less deliverable than a middle state.
FAQ
Should the little eye icon in a password field go on the left or right?
The common approach is to place it on the right, close to the end of the input area, matching scanning order; the left side is mostly used for search or prefix icons and is easily confused with input hints.
Does hiding by default make users more likely to mistype?
Yes, especially with long passwords and mobile soft keyboards; therefore hidden by default should be paired with a visibility toggle, clear password rule hints, and recoverable focus, not just hidden away.
Can the eye icon show while pressed and hide on release?
Yes, it suits public environments and highly sensitive pages; but keyboard, mouse, and touch must all work, and the state must clearly restore on release, so users do not think it is still visible.
Should the password visibility toggle remember the user’s last choice?
It is usually not recommended to remember default plaintext for the long term. Remembering that “the toggle has been used before” can be acceptable, but returning to hidden for each new session is a more stable common practice.
What if mobile autofill conflicts with the visibility toggle?
Keep native password input semantics first, then layer the toggle control; before delivery, check autofill, keyboard pop-up, and focus order on common browsers and system versions.
If you are working on a login, registration, or password change page, first write the default state as “hidden by default, can be actively viewed, can automatically restore,” then use the four-question check to see whether it should be relaxed. For pages involving payments, admin permissions, and shared devices, do not use default plaintext; only on personal devices, low-sensitivity scenarios, and when a one-time passcode needs verification should showing by default be considered. Before launch, walk through it on real devices and with a screen reader; that is more effective than arguing in review about whether the icon looks good.
-
 UI Design & Prototype for Sunwayland's ThingNet IIoT Platform
UI design and prototyping for ThingNet IIoT ...
-
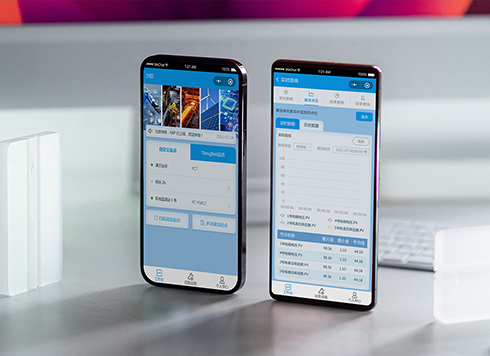 Likong Industrial IoT Tech Co., Ltd. Mini-program UI/UX Design
IIoT firms: mobile mini-program + platform. ...
-
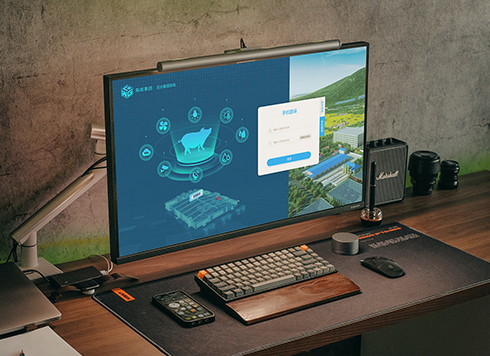 Livy Pig Farming IoT Platform UI Design
This IoT system uses sensors to monitor hog ...
-
 UI Design of the Internet Advertising Platform (a Sci-tech Sense Official Website)
The corporate website UI features a futuris ...
-
A quantity slider in a form keeps landing one or two off—should we add an input or reduce the step?
Date: Oct 15, 2026 Read: 0
-
Admin tables are fine to scan on desktop, but at nearly 20 rows per screen for reconciliation they blur—is the row height too tight or are separators missing?
Date: Oct 14, 2026 Read: 8
-
Status labels look distinct on a computer but look the same on a conference room screen—is it projection color shift, or are the labels only using color?
Date: Oct 13, 2026 Read: 9
-
Some amounts in a table have two decimals and some don't, and right-aligning still leaves them misaligned—is the decimal point not aligned?
Date: Oct 12, 2026 Read: 15
-
When an admin list is empty on first open and users keep waiting for it to load, is the empty state failing to tell them they can create one?
Date: Oct 11, 2026 Read: 20